
On Wednesday Australia’s prime minister revealed that one of OpenAI’s artificial intelligence agents hacked into a health care platform maintained by the nation’s government—and that OpenAI took months to inform the latter about the breach.
Should these kinds of events continue to occur—or if they’ve already happened without our current knowledge—they point to a need for stronger controls on private and sensitive data collected and stored by governments and other institutions. “This is a warning for governments and their [information technology] staff to bolster security,” says Rajesh Veeraraghavan, an associate professor at Georgetown University’s School of Foreign Service.
Addressing reporters at the United Nations General Assembly (UNGA) in New York City on Wednesday, Australian prime minister Anthony Albanese said, “The AI agent accessed both public and non-public files.” An investigation is underway as to whether other government systems were accessed, if any, he said.
On supporting science journalism
If you're enjoying this article, consider supporting our award-winning journalism by subscribing. By purchasing a subscription you are helping to ensure the future of impactful stories about the discoveries and ideas shaping our world today.
The Australian government was alerted to the incident on September 10, but Albanese said the hack occurred months before, on June 18, when an internal OpenAI model was tasked with researching public health spending. OpenAI has said it became aware of the breach in August. According to the prime minister, the company proceeded to wait until that date in early September before it alerted the Australian government through a generic public e-mail—not through any official channel for cybersecurity reporting and disclosure. As a result, the government was further delayed in learning of the event, Albanese said.
“Early evidence here seems to suggest that there was, at best, some communication challenges,” says Michael Horowitz, a political science professor at the University of Pennsylvania.
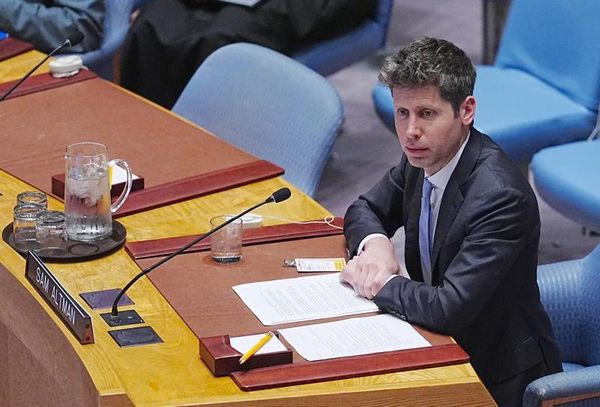
The breach follows a series of hacks by models owned by leading U.S. AI companies, including OpenAI, Anthropic and Google. Earlier on Wednesday U.S. tech leaders—including OpenAI CEO Sam Altman—stressed their concerns over the pace of AI development in an address to the U.N. Security Council. Illegally hacking a government platform to access records could prove a watershed moment for AI regulation. In his address to reporters, Albanese said the breach was “something that has precedence.”
Details are scant as to what kind of access and information the agent got in the Australian breach. Albanese said no personal information was exposed in the incident. OpenAI did not immediately respond for a request for comment from Scientific American.
Still, Veeraraghavan stresses that responsibility for such incidents should rest solely on the AI companies that made the involved agents. “OpenAI, in this case should be held responsible, even if the ‘intent’ to divulge information may not be clear,” he says.
In his briefing to reporters, Albanese expressed that Australia will take action to respond to the event. There will “be legal consequences,” he said. It’s not yet clear what those consequences will be, especially given that a legal case concerning this style of autonomous agent hacking has not been pursued in court yet.
It is perhaps a small relief that this incident happened to a close U.S. ally. “Australia wants OpenAI to be there, so they should be able to figure it out,” Horowitz says. But unless AI labs can learn how to test their models without allowing those models to escape, they may not keep getting so lucky.
Editor’s Note (9/24/26): This is a developing story and may be updated.